Data Masking in the BFSI Sector
The Banking, Financial Services, and Insurance (BFSI) sector handles large volumes of personally identifiable information (PII), non-public information (NPI), and sensitive financial data every day. This information includes national identification numbers, account details, credit scores, financial transactions, and loan documents.
Protecting this data is a critical responsibility for banks, insurance providers, and other financial institutions. Sensitive information must remain secure not only in production systems but also in development, testing, storage, analytics, and data-sharing environments.
Data masking helps financial institutions protect sensitive information by replacing, obscuring, or transforming original values while preserving the data characteristics needed for authorized business activities. Depending on the masking method, organizations can maintain realistic data formats and relationships without exposing actual customer information.
The following five use cases illustrate how data masking supports privacy, regulatory compliance, application development, operational security, and digital transformation in the BFSI sector.
1. Protecting Test Data in DevOps and QA
Banks and insurance companies continually modernize their digital infrastructure. Projects may involve developing mobile banking applications, customer service platforms, payment processing systems, or back-office automation tools.
These applications require thorough testing in environments that closely resemble production. However, copying unprotected customer information into development and QA systems creates unnecessary exposure risks.
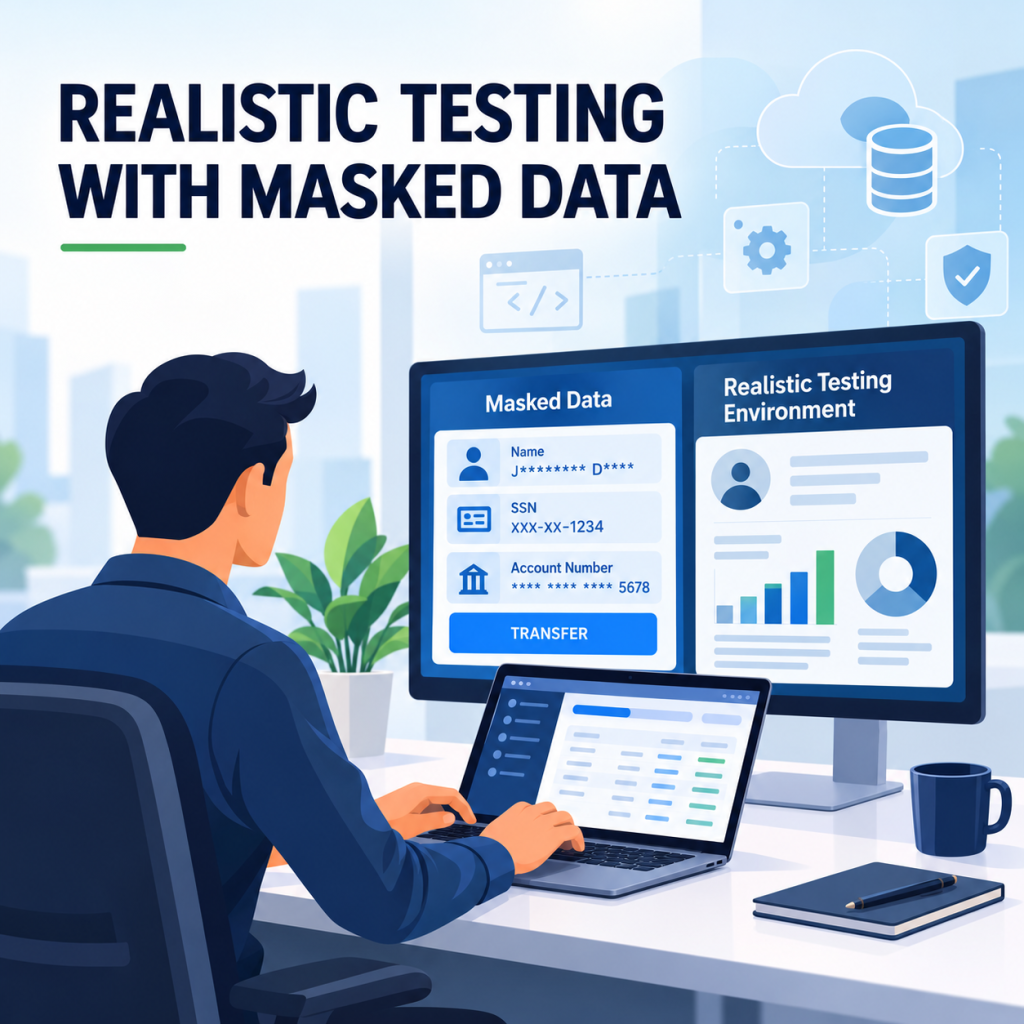
Data masking allows development teams to work with realistic datasets without disclosing actual account numbers, card information, Social Security numbers, or other sensitive values. As a result, teams can test application functionality, scalability, and performance while reducing the exposure of confidential financial information.
Preserving Data Realism and Referential Integrity
Realistic test data is particularly important in financial systems because applications frequently depend on relationships among customers, accounts, transactions, and other records.
Static data masking techniques, such as format-preserving encryption (FPE), scrambling, pseudonymization, and blurring, can transform sensitive values while preserving selected characteristics needed for testing.
For relational database testing, maintaining referential integrity is equally important. Related records must remain consistently linked after masking so that database relationships continue to function correctly.
When test environments include multiple databases or disparate data sources, deterministic masking functions help maintain consistency. For example, financial institutions can discover matching classes of sensitive information across data sources and apply the same masking rules. This approach helps ensure that identical original values receive consistent masked representations wherever those rules are used.
How IRI FieldShield and DarkShield Support BFSI Test Data
Many BFSI implementations of IRI data masking tools focus on test data protection. For example, several regional banks in the US and federal financial ministries abroad use IRI FieldShield to classify and consistently de-identify NPI, including account numbers and amounts, along with PII in lower relational database environments.
These projects also involve legacy files and financial transaction formats, including Automated Clearing House (ACH) and Fedwire files. In these environments, realistic masking and referential integrity are important to the usability of the resulting test data.
Realistically masked data is also important in DevOps and quality assurance projects involving masked data subsets, PDF and Microsoft Office documents, and PII embedded in images. Data masking tools like IRI DarkShield can find sensitive information in these sources and apply the same masking rules across structured, semi-structured, and unstructured test targets.
2. Sharing Data Across Business Units
BFSI companies often operate across multiple departments, subsidiaries, and business units. Information regularly moves between teams responsible for risk analysis, customer segmentation, fraud detection, reporting, and business intelligence. Although these activities depend on access to relevant data, sharing complete customer records can unnecessarily expose sensitive financial and personal information.
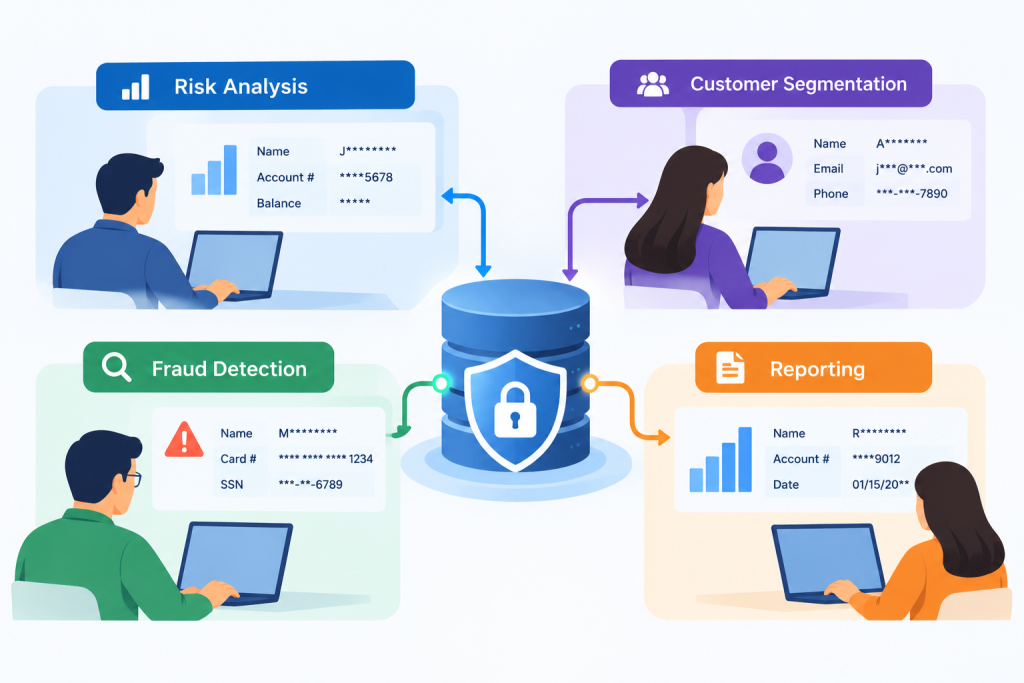
Data masking helps companies limit that exposure by providing transformed or selectively redacted data to the teams that need it. Depending on the system and access requirements, companies can use role-based masking and selective redaction to restrict the visibility of sensitive fields without preventing legitimate business activities.
Data Masking Methods for Secure Data Sharing
There are several ways to mask specific classes of data in on-demand scenarios while leaving production data unchanged. These include:
- Dynamic data masking: Queries against relational database (RDB) columns are intercepted and evaluated for authorization. Unauthorized values are redacted using methods like these.
- Dynamic data unmasking: Production data at rest remains encrypted, while API calls from authorized users reveal decrypted values, as shown in this example.
- Incremental data masking: Source rows that are inserted, updated, or deleted are masked or removed from target tables in real time, following this method.
- Shared subsets: Files are masked during filtering for specific uses, or smaller, referentially correct table subsets are masked during the subsetting process, as shown here.
3. Mitigating Third-Party Risk
Banks, insurers, and other financial organizations rely on external service providers for many business functions. These partners may include credit bureaus, call centers, IT service providers, compliance auditors, and other organizations that process financial information on behalf of institutions.
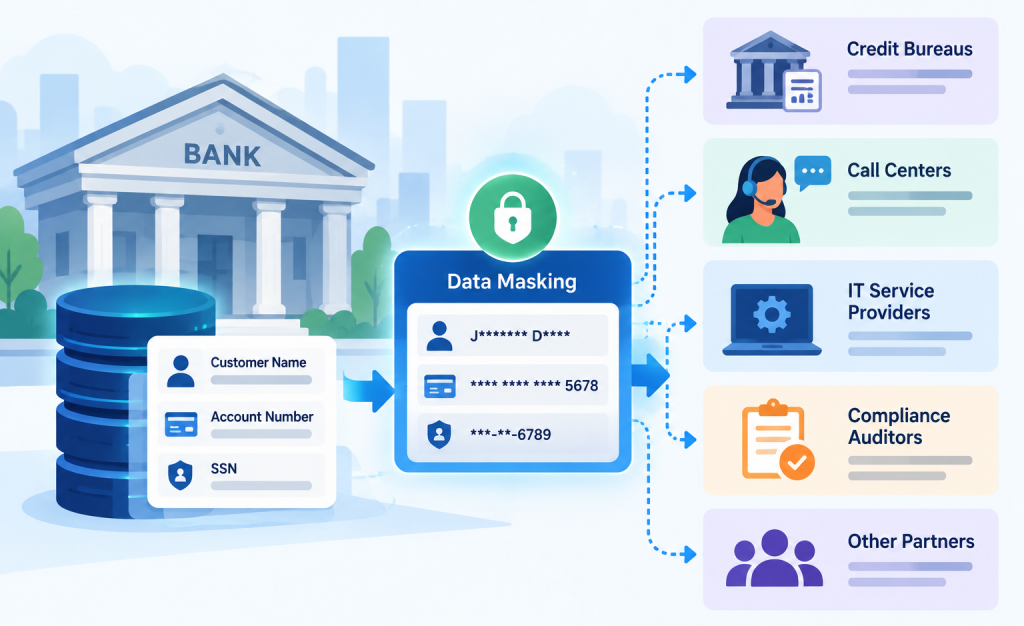
While these relationships support essential operations, transferring sensitive datasets outside an organization’s direct control can increase security and privacy risks. A third-party data breach, compromised account, or insecure access configuration can expose customer information even when contractual security requirements are in place.
In fact, many publicly reported data breaches affecting financial institutions involve cyberattacks or insecure access to data held by third-party data processing partners. Each week, IRI shares reports of such breaches and discusses how data masking could potentially reduce their impact on its LinkedIn page here.
Masking Sensitive Data Before External Sharing
Data masking reduces unnecessary exposure by transforming sensitive values before datasets are shared with external partners.
Instead of receiving actual customer identities, account information, or other protected financial records, third parties can receive masked information that supports the intended business activity. This approach can reduce the consequences of unauthorized access to shared datasets while allowing legitimate operations to continue.
Classification-Based Masking Across Different Data Sources
BFSI companies can use classification-based masking to protect sensitive data in relational databases, NoSQL collections, documents, images, and other files. By identifying and masking sensitive information before it leaves your firewall, financial institutions can reduce the risk of exposing customer data to third parties.
4. Complying With Data Privacy Regulations
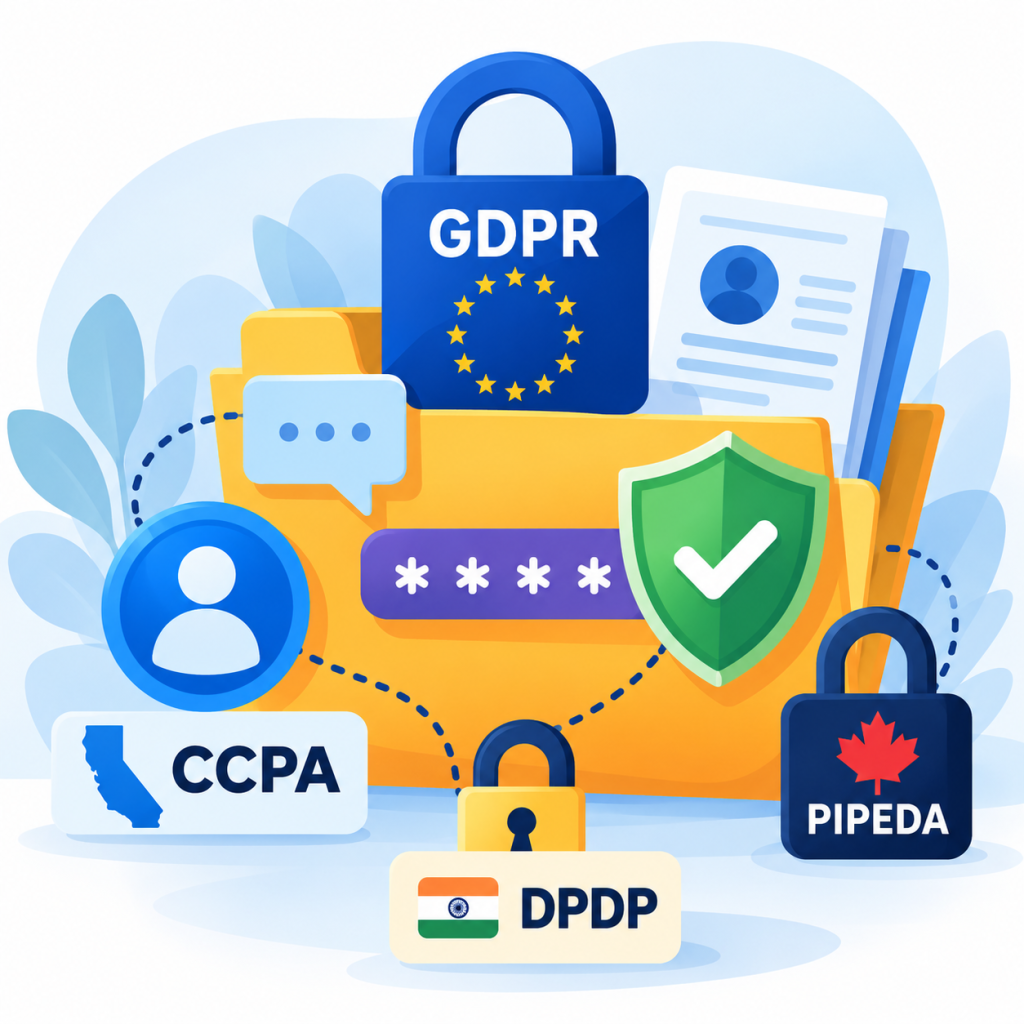
Financial institutions operate under overlapping industry-specific security standards and privacy regulations. Depending on their operations, locations, and the information they process, relevant requirements may include:
- Gramm-Leach-Bliley Act (GLBA)
- Payment Card Industry Data Security Standard (PCI DSS)
- Sarbanes-Oxley Act (SOX)
- General Data Protection Regulation (GDPR)
- California Privacy Rights Act (CPRA)
- Personal Information Protection and Electronic Documents Act (PIPEDA) in Canada
- Digital Personal Data Protection (DPDP) Act in India
These frameworks address different aspects of financial reporting, privacy, information security, data governance, and the protection of sensitive information. Although their specific requirements vary, they reinforce the importance of appropriate access controls and responsible handling of protected data.
How Data Masking Supports Compliance
Data masking can help financial institutions implement safeguards that support applicable privacy and security obligations. For example, organizations may redact payment card numbers, pseudonymize personal information, or transform sensitive financial attributes before data is used in development, testing, analytics, or external sharing.
However, masking methods must be selected according to the applicable requirements and the intended data use. Pseudonymized or reversible data may still be considered personal data under relevant privacy laws. Similarly, masking does not automatically fulfill data deletion obligations such as those associated with the GDPR right to erasure.
Financial institutions should therefore treat masking as part of a broader data governance and compliance program rather than as a complete substitute for other controls.
Maintaining Data Usability While Protecting Privacy
Certain masking approaches, including format-preserving encryption and pseudonymization, can retain useful characteristics of original data. This allows organizations to support testing and analytics requirements while reducing exposure of sensitive values.
You can learn more about masking for compliance from these IRI resources:
What Is the Payment Card Industry Data Security Standard (PCI DSS)?
Navigating DPDPA Compliance
Strengthening GDPR Compliance
Right to Erasure Requests
5. Securing Cloud Migrations, Big Data, and AI Initiatives
With the growing adoption of cloud platforms and big data tools, BFSI companies increasingly use cloud-based infrastructure for everything from customer insights to credit risk models. However, using unmasked production data in cloud environments can expose sensitive customer information.
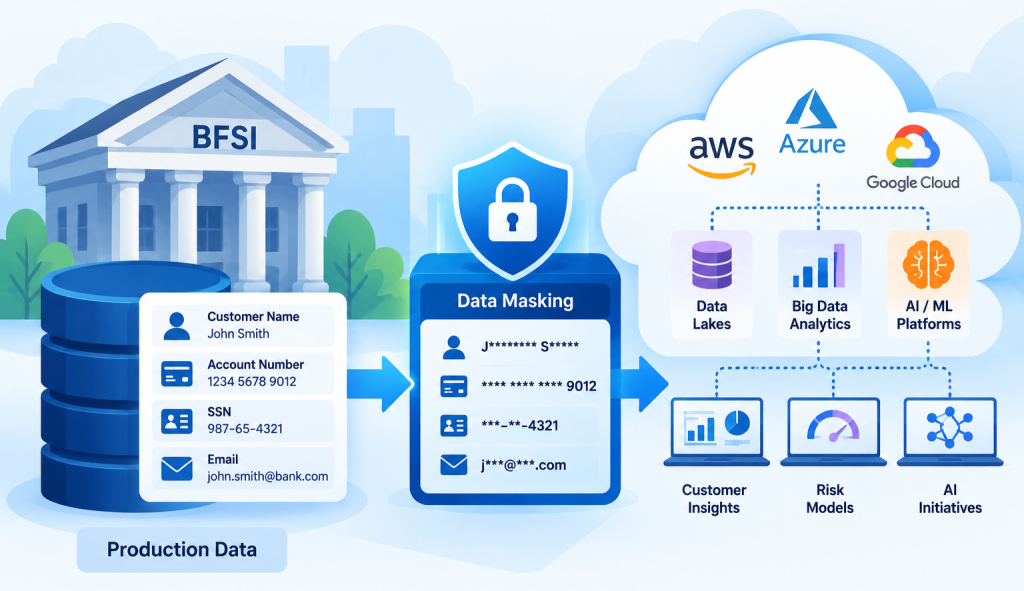
Masking sensitive data before migration or analysis allows cloud tools and services to perform their intended functions without accessing actual customer information. This is especially important when working with external data lakes, AI/ML platforms, or global data teams.
For more information, see these resources from Bloor Research articles and IRI:
IRI Data Migration and Modernization
Data Governance and Security in the Age of AI
A Smart Investment in Data Governance
For the BFSI sector, data masking supports more than individual privacy requirements. It contributes to broader goals involving data governance, operational resilience, secure collaboration, and digital modernization.
When implemented appropriately, masking helps financial institutions reduce exposure of sensitive information while retaining data utility for development, testing, analytics, and other authorized activities.
For more information on data security, data privacy laws, and data masking concepts, visit the IRI Data Education Center at: https://www.iri.com/support/data-education-center. For sites using IRI software in financial institutions, visit: https://www.iri.com/customers/industries/bfsi.
Frequently Asked Questions (FAQs)
What is data masking in the BFSI sector?
Data masking in the BFSI sector protects sensitive customer and financial information by transforming or obscuring original values. It allows banks, financial service providers, and insurance companies to use protected datasets for testing, analysis, and sharing without unnecessarily exposing original information.
How does data masking improve DevOps and QA testing in BFSI organizations?
Masked datasets simulate production environments without exposing real customer data, allowing developers and QA teams to test applications safely. Applying format-preserving encryption and unique pseudonymization functions consistently to pre-classified data helps maintain referential integrity across multiple databases and systems.
What types of data can be masked in financial institutions?
Financial institutions can mask personally identifiable information (PII) and sensitive financial details such as names, addresses, Social Security numbers, credit card numbers, account balances, and transaction parameters. These values may appear in structured, semi-structured, and unstructured sources, including databases, PDFs, images, and legacy mainframe files.
How can data masking support secure information sharing across business units and third-party vendors?
Role-based masking, selective redaction, and other masking methods help financial institutions limit the exposure of sensitive information when sharing data internally or with external vendors. Authorized teams can access the information needed for risk analysis, fraud detection, and business intelligence, while third parties can work with appropriately masked datasets without accessing unnecessary customer identities or financial records.
What regulatory requirements can data masking help BFSI companies meet?
Data masking can support compliance with applicable requirements under PCI DSS, GLBA, SOX, GDPR, CPRA (CCPA), PIPEDA, KVKK, and India’s DPDP Act. Techniques such as pseudonymization, redaction, and other appropriate data transformations help protect sensitive information. However, masking alone does not guarantee regulatory compliance or automatically satisfy requirements such as GDPR’s right to erasure.
How does data masking support cloud migrations, big data, and AI projects?
Masking sensitive data before cloud migration or use in AI/ML platforms helps protect customer information in external or shared environments. This allows financial institutions to support cloud analytics, credit risk modeling, and big data initiatives while reducing unnecessary exposure of original financial records.
How can BFSI organizations preserve data realism and consistent masking across multiple systems?
Format-preserving encryption (FPE), deterministic pseudonymization, and blurring can preserve selected data characteristics needed for testing and analysis. By applying consistent masking rules and deterministic functions to related datasets, organizations can maintain referential integrity across databases, files, and other systems where supported by the chosen transformations.
Can IRI FieldShield and DarkShield mask both structured and unstructured BFSI data?
Yes. IRI FieldShield supports masking structured data, including relational database tables and flat files. IRI DarkShield can discover and mask sensitive information in structured, semi-structured, and unstructured sources, including NoSQL databases, EDI files, PDF and Microsoft Office documents, Parquet files, SQL files, logs, free text, and images. Together, these tools support financial data protection across different data sources and environments, including on-premises and cloud deployments.