Payment Card Security Challenges
Per every Experian industry forecast in the last five years, the number of data breaches will continue to rise. Ponemon Institute studies of data breaches reveal that the average cost to a US organization exceeds $200 for each compromised customer record.
With an average of 29,000 records compromised per incident, the cost of a data breach in this country can reach well over $5 million. In 2023 alone, the global average was $4.45M per breach, according the same Ponemon study IBM annually comissions.
In addition to the significant financial harm that results from a data breach, there is an acute loss of trust between an organization and its customers. Both the breach and the fallout are usually well publicized and long remembered.
And although the most expensive data breaches are in the healthcare sector, protecting payment card information is still a major issue because credit card numbers and account holder PII is routinely subject to hacks, theft, fraud and other misuse.
According to this SecurityMetrics analysis of Payment Card Industry (PCI) Data Breaches, despite the fact that 12 documented PCI 2.0 Data Security Standard (DSS) requirements were largely in place, external (50%), internal (33%) breaches still continued. The trend is worsening as the definitions of the 3.x and 4.x standard widens to include more forms of PII.
PCI DSS Compliance Solutions
To help mitigate or even nullify the effects of data breaches, and help BFSI companies and other organizations managing credit card data comply with PCI DSS requirements, the data discovery and masking functions in IRI Data Protector Suite products -- or the IRI Voracity platform -- find and protect primary account number (PAN), and other credit card number values (plus other data at risk) in multiple data sources.
These IRI data masking tools support PCI DSS rules for data-centric security through credit card data encryption, SHA-2 cryptographic hashing, and/or tokenization functions.
For example in structured data sources like normal form relational database columns and fields in flat files, IRI FieldShield users apply their choice of data classification, search methods, and data-centric security functions to PANs and other sensitive data in an intuitive, efficient, and flexible manner under Eclipse. For example, specification of an encryption cipher with a pass-phrase occurs in a simple dialog:
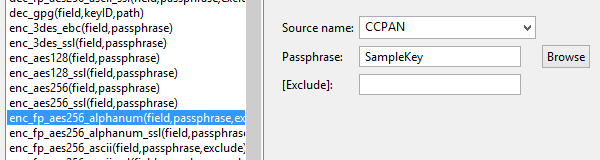
Here, format-preserving encryption is used for PCI DSS compliance, and to ensure that no changes are required to the table or database structure. Keeping the original look and feel to the values can also sometimes deceive hackers into thinking they have actual PANs.
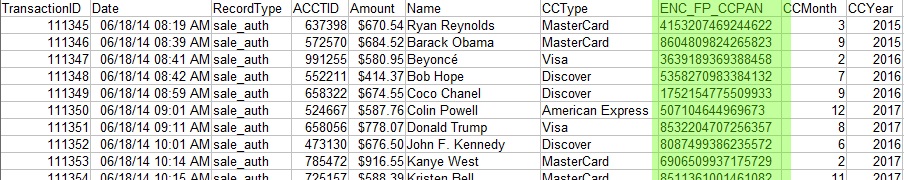
These easy, yet powerful static data masking functions can also help you limit the financial and operational impact of a data breach. For example, Steam, a gaming distribution platform, suffered a data breach. As significant as the breach was, the overall impact to Steam was limited because the credit card values were encrypted.
FieldShield and the other IRI data masking tools (DarkShield for multiple forms of semi- and unstructured data, and CellShield for Excel spreadsheets) -- which share data classification, scanning, and data masking rules -- provide simplicity, affordability, and peace-of-mind by finding and securing credit card data and other PII at rest.
These proven data masking tools help organizations like this one meet PCI DSS requirements for protecting stored cardholder data, while mitigating the risk of data loss and providing safe, intelligent test data targets. In other words, data masking solutions for PANs have become recognized payment card security best practices.
It is also possible to encrypt/decrypt or redact PANs or PII in a dynamic data masking context, through an application that queries a database, for example.
Now consider the PAN skimming threat from AI agents. In this late 2026 example of the Strix / Cairn / Hermes AI-driven campaign, threat actors used a chained trio of open-source AI agent frameworks to autonomously scan for vulnerabilities, exploit online retailers, inject e-skimmers, and exfiltrate over 600,000 credit card records. At one victim site, an AI-driven "Database Wipe" skill over-reached, completely destroying 180 database tables and backups.
Deploying IRI DarkShield, the enterprise data discovery and masking product, helps mitigate the fallout of a similar autonomous AI breach through several critical data-centric defenses:
- Automated De-identification: IRI DarkShield continuously scans structured databases, semi-structured logs, and unstructured text files to discover Personally Identifiable Information (PII) and payment card industry (PCI) data.
- Format-Preserving Encryption (FPE) & Masking: By automatically masking, hashing, or encrypting credit card numbers at rest, the data becomes useless to attackers. If an AI agent exploits a system and exfiltrates the tables, they only steal structurally valid but entirely simulated or strongly encrypted strings, preventing financial fraud and lowering compliance liabilities under PCI-DSS or GDPR.
- Decoupling Production Data from Vulnerable Apps: IRI DarkShield (often bundled within the IRI Voracity platform) is frequently used to generate highly realistic, synthetic, or heavily masked test data environments. Keeping actual sensitive records out of standard web-facing retail tiers means an automated destructive script cannot touch your crown jewels.
- Granular Restructuring: If encryption rules are bound tightly to data classes at the ingestion layer using DarkShield, applications do not need to store raw fields in plain text tables that are highly susceptible to mass automated
DROP TABLESQL injections or broad regex wipes.
- Cross-Silo Coverage: Unlike basic security tools that only protect relational databases, IRI DarkShield simultaneously targets relational and NoSQL databases (like Oracle, Snowflake, Salesforce, CosmosDB and MongoDB), flat files, PDF attachments, and images.
- Catching E-Skimmer Leaks: If a skimmer scripts or copies transaction data into hidden text files or local server logs prior to exfiltration, DarkShield’s automated API schedules can catch, alert, and mask those raw text leaks before the threat actor draws them out of the network.
- Audit-Ready Telemetry: DarkShield outputs machine-readable JSON and delimited search/mask logs.
- Rapid Anomaly Detection: These logs can be immediately piped into SIEM or analytics platforms like Splunk ES or Datadog. If DarkShield suddenly registers an unexpected surge of sensitive data cropping up in web server caches or temporary directories—a classic sign of an active AI extraction and skimming agent—defenders can isolate the compromised environment before mass exfiltration finishes.
You can learn more about PCI DSS solutions in these top data masking tools through a live demo or free trial.
Blog Links
